Let your teams use AI agents. Keep control of what they touch
See every AI agent. Check every action against its task. Prove every decision. On the laptops, servers, browsers and cloud your agents run on.
NewAgentic Security Pedia: what to ask about every AI agent

Your AI agents run with your keys
Coding agents, assistants and in-house bots read source code, open secrets, call tools and send data with the access of whoever runs them. Most of it goes unseen, and the logs blame the person.
keys left one company's laptops inside ordinary agent requests in 19 days. None looked like an incident.1
installed coding agents had no recorded session. A dormant agent is what the Nx supply-chain attack used.1
actions recorded on one company's laptops. No person can review that by hand.1
public reports of coding-agent incidents and security findings in our sourced dossier, from wiped databases to stolen keys.2
1. GIRD case study: 19 days on one company's laptops, observation mode, anonymised. 2. GIRD incident dossier: publicly reported coding-agent incidents, each with its source.
One control plane for your whole agent estate
GIRD runs where your agents run, sees what they do from the operating system up, and decides every action against one policy. Everything lands in one record.
Find every agent, sanctioned or not
GIRD inventories every AI agent, MCP server and model your teams use, ties each one to a person and a team, and flags the ones nobody approved.
- Shadow agents found the day they appear
- Every agent mapped to an owner and a team
- Agents, tools and models in one registry
Know what each agent was asked to do, and what it did
GIRD joins what an agent reports through its hooks with what the operating system sees it do, and checks every step against the task the developer gave it. A step that has nothing to do with the task stands out at once.
- Every prompt, tool call, file, command and connection in one session
- Each step scored against the task, on the device
- The full path from prompt to action, for any investigation
- 1
read payments/refund_test.goIn task - 2
run go test ./payments/...In task - 3
edit payments/refund.goIn task - 4
read ~/.aws/credentialsBlocked - 5
curl paste.example.netBlocked - 6
git push origin fix/refund-flakeIn task
Decide every action, below the agent
Policies run in the operating system, not just inside the agent. An agent with no hooks, or with its hooks turned off, is governed all the same. Every action is allowed, blocked, redacted or sent to a person for approval, right on the device.
- Least privilege for every agent, by team and by task
- No round-trip to a cloud for a decision
- Approvals in Slack or Teams for the actions that need a person
Spot the agent that breaks its own pattern
GIRD learns how each agent normally works: its tools, files, hosts and commands. When one steps outside that baseline, you see it in seconds, with the session that led there. GIRD's own models, trained on agent and operating-system telemetry together, classify what is happening. Your policy decides what is allowed.
- A baseline for every agent, on every device
- Alerts on behaviour, not just on known bad strings
- One view of risk across the whole fleet
Keep secrets, personal data and confidential work inside
Keys, personal and sensitive personal data, and confidential documents are found and redacted before an agent sends them anywhere. Detection runs on the device, so a prompt never leaves it to be checked.
- Secrets and tokens from every major provider
- PII and SPI, including Aadhaar, PAN and card numbers
- Your confidential documents, matched by meaning, not file name
Refund order 88213 for priya.s@example.com, card 4111 1111 1111 1111, PAN ABCDE1234F. Use key sk-live-9f2c... and attach Q3 board pack.pdf.
Refund order 88213 for EMAIL, card CARD, PAN PAN. Use key SECRET and attach BLOCKED: CONFIDENTIAL.
Evidence for every decision
Every decision lands in a tamper-evident record, tied to a person, an agent and a policy, and streams to your SIEM. Controls map to the frameworks and rules you already report against.
- Answer "which agent did this, and who ran it" in seconds
- Evidence packs for audits and regulators
- Retention set to your rules, kept in your region
- Time
- 25 Oct 2026, 14:02:11 IST
- Agent
- Claude Code
- Person
- p.nair · Payments
- Task
- Fix the flaky refund test
- Action
- read ~/.aws/credentials
- Policy
- Payments · Credentials
- Decision
- Blocked, outside the task
Works with what you already run
Rolled out through your MDM. Tied to your identity provider. Streaming to your SIEM. Running next to your EDR. Engineers install nothing.
- Your MDM
- Jamf, Microsoft Intune, Kandji and Workspace ONE push GIRD to every laptop.
- Identity
- Okta, Microsoft Entra ID and Google Workspace give every agent a person, a team and a policy.
- SIEM and SOAR
- Splunk, Microsoft Sentinel, Datadog and Google SecOps get every decision as it happens.
- Your EDR
- Runs alongside CrowdStrike Falcon, SentinelOne and Microsoft Defender.
- Workflow
- Approvals and alerts in Slack, Microsoft Teams, Jira and ServiceNow.
- Servers and cloud
- AWS, Azure and Google Cloud report to the same control plane.
19 days on one company's laptops
GIRD watched one company's engineering laptops in observation mode, blocking nothing. Keys left inside ordinary agent requests, and more than half the installed agents never ran a session, yet stayed installed.
Read the case studyBuilt for regulated teams, by people who have been audited
Decisions on the device
Policy runs on the laptop or server. No round-trip to a cloud for a verdict.
Your data, your region
Choose where records live and how long they stay. Prompts are checked on the device.
Tamper-evident record
Every decision is sealed into a chain you can verify.
Never stalls engineering
If GIRD itself stops, your teams keep working.
Signed builds
Rolled out through your MDM. Mac builds are notarized by Apple.
Security reviews
We complete your CAIQ, SIG or own questionnaire.
Disclosure
We acknowledge reports within 2 business days and fix high-severity issues within 30. Policy.
Trust Center
What we collect and never collect, where it lives, and who processes it, in one place.
The team
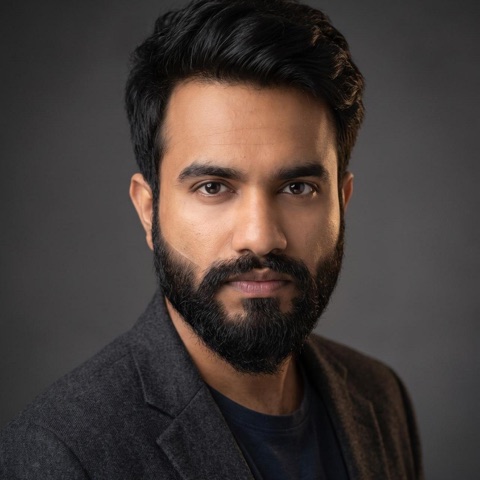
Akash Shaw
Seven years building the systems regulators audit. At CRED he owned a lending platform doing 100,000+ loans a day under RBI supervision, and let AI agents write its production code for nine months under guardrails he wrote.
Understand the risks before you buy anything
What is agentic AI security?
The risks agents add, the controls that answer them, and what auditors ask.
Incident dossier47 coding-agent reports, sourced
What went wrong, and what would have stopped it.
For your engineersBlindspot
An open-source, read-only check for the AI keys and agents on one computer.
Try Argus on your own Mac
See every AI coding agent on your Mac and where it connects. The community edition runs on one Mac. For a team, roll it out through your MDM and run it from the GIRD console.
See what your agents are doing this week
Thirty minutes with a founder. Bring the agents your teams use, and see what GIRD finds and what your first policy looks like.
or write to hello@gird.ai